Effective 18 November 2026.
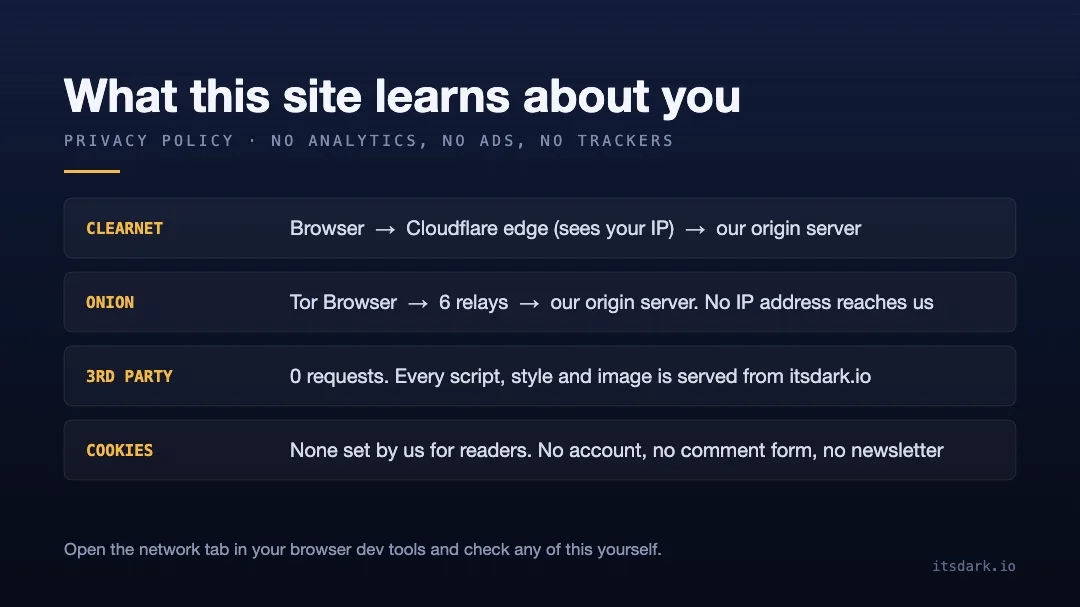
The short version: itsdark.io runs no analytics, no advertising and no third-party scripts. You cannot create an account, post a comment or subscribe to anything. The only data that exists about your visit is a line in a server log, and you can avoid even that by using our onion mirror.
The rest of this page is the long version. It is written to be checked. Where we make a technical claim, we tell you how to verify it from your own browser.
Who is responsible for your data
itsdark.io is an independent publication operated from Panama. For the purposes of data protection law, the operator of itsdark.io is the controller of the limited data described here. The contact address for anything on this page is [email protected]. Put [legal] in the subject line so the request is routed correctly.
What happens when you load a page
A privacy policy is easier to trust when you can see the request path, so here it is.
Over the regular web (https://itsdark.io)
- Your browser opens a TLS connection to Cloudflare, which we use as a reverse proxy for DDoS protection and caching. Cloudflare terminates TLS, so it necessarily sees your IP address, the URL you request and your browser’s request headers.
- Cloudflare forwards the request to our origin server. Most page views are answered from a cache in front of WordPress and never reach the application or its database.
- The origin server writes a standard access log entry: timestamp, requested path, HTTP status, response size, referrer, user agent, and the client IP address passed on by Cloudflare.
That log entry is the only record we hold of an ordinary visit. We use the logs to diagnose faults and to detect abuse such as credential stuffing against the login page. Logs are rotated and overwritten by the server’s log rotation, are not copied into any analytics product, and are not combined with any other data set. We do not build visitor profiles, and we have no way to tell that two visits came from the same person other than the IP address and user agent in those lines.
Over Tor (the .onion mirror)
The site is also published as a v3 onion service. The address is in the footer of every page. When you use it, your connection travels through a six-relay rendezvous circuit and reaches our server without any IP address attached. Onion traffic does not pass through Cloudflare. In that mode we receive a request path and whatever headers Tor Browser sends, which are deliberately identical for every Tor Browser user. There is nothing in that request we could use to identify you, and that is the point of offering it.
What we do not do
- No analytics. No Google Analytics, no tag manager, no “privacy-friendly” hosted analytics, no session recording, no heatmaps.
- No advertising. No ad networks, no retargeting pixels, no sponsored widgets.
- No third-party requests. Scripts, stylesheets, images and icons are all served from itsdark.io. Typography uses your system fonts, so there is no font CDN. There are no embedded videos, maps or social widgets.
- No fingerprinting. We do not run canvas, audio, WebGL or font-enumeration probes, and we do not ask your browser for any permission.
- No accounts, comments or newsletter. Comments are closed across the site, so the comment-related data collection that a default WordPress install performs (name, email, IP address, Gravatar hash) does not happen here.
Verify it: open your browser’s developer tools, switch to the Network tab and reload any page. Every request should go to itsdark.io. If you ever see another hostname, that is a bug and we want to hear about it.
Cookies and local storage
We set no cookies for readers and write nothing to local storage. That is why there is no cookie banner: there is nothing to consent to.
Two exceptions exist, and neither is used for tracking:
- Cloudflare security cookies. If Cloudflare decides a request looks automated, it may present a challenge and set a strictly necessary cookie such as
__cf_bmorcf_clearanceso that you are not challenged again on the next page. These are set by Cloudflare, expire on their own, and are covered by Cloudflare’s privacy policy. - Staff login cookies. WordPress sets session cookies for our own editors when they sign in to the admin area. Readers never receive these.
Site search
If you use the search box, the search term is sent to our server as part of the URL and therefore appears in the access log like any other request path. We do not keep a separate record of searches.
If you write to [email protected], we receive your email address, the message, any attachments and the technical headers your mail provider adds. We use that information to reply and to act on what you reported, for example to correct an article or review a Sonar Index entry.
Correspondence stays in our mailbox while the matter is open. We delete it once it is resolved, unless we need to keep a record: a legal notice, or the evidence behind a published correction. We never publish a correspondent’s name or address without permission, and the corrections log does not identify who reported an error.
Email is not anonymous. If your identity is sensitive, the contact page has practical advice on writing to us safely.
Outbound and affiliate links
Articles link to external sites. When you follow a link, your browser tells the destination that you arrived from https://itsdark.io/. Modern browsers send only that origin across sites, not the full address of the article you were reading. From that point the destination’s own privacy policy applies.
Some links are affiliate links. They carry an identifier for itsdark.io, not for you, and they are labelled next to the link. If you buy something, the merchant tells us that a sale happened and what commission it earned. The merchant does not tell us who you are, and we do not ask. See the affiliate disclosure.
The Sonar Index
Sonar makes outbound requests from our server to the onion services it lists. It does not involve your browser. Viewing the index does not cause your device to contact any listed service, and the status badges are plain HTML rendered on our side.
Who else touches the data
| Party | Role | What it can see |
|---|---|---|
| Cloudflare, Inc. | Reverse proxy, caching and DDoS protection for the clearnet site | IP address, requested URL, request headers |
| Our hosting provider | Runs the origin server | The server’s disks, including access logs |
| Our email provider | Hosts the [email protected] mailbox | Messages you send us |
These providers act on our instructions and may process data outside Panama and outside your own country. We do not sell, rent or trade personal data, and we do not share it with data brokers or advertisers. There is no data set here worth selling.
Legal requests
We will disclose data only in response to a valid, binding legal order from a court or authority with jurisdiction over us in Panama, and we will read any such order narrowly. In practice there is very little to hand over: server log lines for clearnet visits and whatever is in our mailbox. For visits over the onion mirror we hold no identifying data at all.
Legal basis and your rights
Our handling of personal data is governed by Panama’s Law 81 of 2019 on Personal Data Protection and its regulation, Executive Decree 285 of 2021. We process server logs on the basis of our legitimate interest in keeping the site secure and available, and we process email on the basis of your request for a reply.
Under Law 81 you have the ARCO rights: access to the data we hold about you, rectification of inaccurate data, cancellation (deletion), and opposition to processing, together with the right to data portability. If you are in the European Economic Area, the United Kingdom or another jurisdiction with comparable rules such as the GDPR, we extend the equivalent rights to you, including the right to restrict processing. If you are a California resident: we do not sell or share personal information as those terms are defined in the CCPA.
To exercise any of these rights, email [email protected] with [legal] in the subject. We do not charge for requests. To locate log entries we need the IP address and approximate time of the visits in question, because we hold nothing else that links a log line to a person.
If you believe we have mishandled your data, you can complain to Panama’s data protection authority, the Autoridad Nacional de Transparencia y Acceso a la Información (ANTAI), or to the supervisory authority where you live. We would appreciate the chance to fix the problem first.
Children
itsdark.io is written for a general adult audience and is not directed at children. Because we collect no account, profile or contact data from readers, we do not knowingly hold personal data about anyone under 16.
Security
The clearnet site is served only over HTTPS. Administrative access requires two-factor authentication. The software is kept patched, and the attack surface is small by design: no reader accounts, no forms and no user-generated content. No system is perfectly secure, and if you find a weakness in ours, please report it to [email protected] with the tag [security].
Changes to this policy
If we change how the site handles data, we will update this page and its effective date before the change takes effect. If we ever add a feature that collects something new, such as a newsletter, it will be opt-in and documented here first. Related documents: terms of use, disclaimer and about itsdark.io.
